Educational Resources
The Impact of Digital Twins in Oil & Gas Plant Maintenance
The Impact of Digital Twins in Oil & Gas Plant Maintenance is a topic that deserves thorough explora...
TAMFIS NIG LTDRC 8067447CAC ACTIVEFinima, Bonny Island, Rivers State
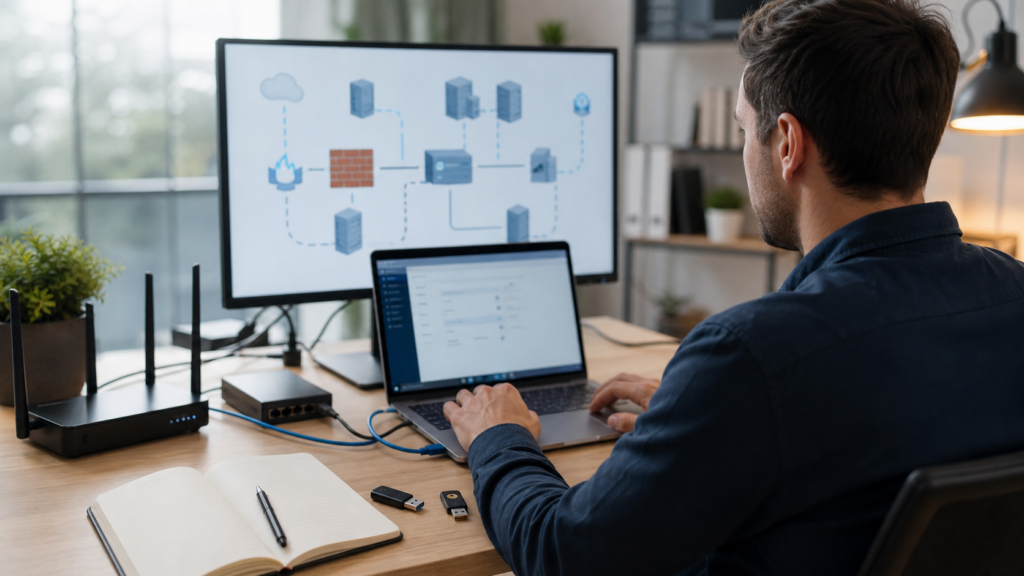
Information security is the disciplined protection of information and the systems that store, process or transmit it. It is broader than installing antivirus software and different from trying to predict every attack. Effective security begins by understanding what matters, how it could be harmed and which safeguards reduce risk without preventing legitimate work.
Beginners often meet a confusing catalogue of products and acronyms. Start with principles. Identify important data and services, control access, maintain systems, watch for abnormal activity, prepare a response and practise recovery. Technology supports these activities, but responsibility, training and documented decisions are just as important.
Confidentiality means information is disclosed only to authorised people or processes. Integrity means it remains accurate, complete and protected from unauthorised change. Availability means authorised users can obtain it when needed. A payroll database exposed publicly loses confidentiality; altered bank details lose integrity; an unrecoverable outage destroys availability.
Controls can support more than one objective. Strong access control protects confidentiality and integrity. Backups can restore availability after deletion, but only if they are protected from attackers and tested. Security decisions should also consider authenticity, accountability, privacy, safety and legal obligations.
An asset is something valuable, such as customer records, credentials, a production service or reputation. A threat is a circumstance capable of causing harm. A vulnerability is a weakness that could be exploited, and risk reflects likelihood and impact. These definitions help teams prioritise rather than treating every technical finding as equally urgent.
Ask which business or personal activity depends on the asset, who owns it, where copies exist and what a realistic failure would cost. Reduce risk by avoiding an activity, applying safeguards, transferring part of the risk or consciously accepting the remainder through an authorised process. No control removes all uncertainty.
The NIST Cybersecurity Framework 2.0 organises outcomes under Govern, Identify, Protect, Detect, Respond and Recover. Govern establishes direction and accountability. Identify develops understanding of assets and risks. Protect applies safeguards. Detect finds possible events. Respond contains and manages incidents, while Recover restores capabilities and incorporates lessons.
These functions are concurrent, not a one-time sequence or product checklist. An organisation that buys protective tools but has no asset inventory, response authority or tested recovery plan remains fragile. Small teams can use the same logic at an appropriate scale.
Authentication establishes who or what is requesting access; authorisation decides what that identity may do. Multifactor authentication reduces risk from a stolen password but does not excuse weak recovery processes or excessive privileges. Attackers may target help desks and account-reset channels, so identity verification must cover the entire account lifecycle.
Keep an inventory of supported devices, applications and owners. Apply security updates through a controlled process, remove software that is no longer needed and replace products that cannot receive fixes. Use secure configurations, screen locking, storage encryption and endpoint protection appropriate to the environment.
Do not expose administrative services directly to the internet without a justified, secured design. Segment networks so one compromised device does not automatically reach every system. Protect routers and wireless access points with current firmware, strong administration credentials and documented configuration backups.
Collect only information that serves a defined purpose. Classify it, restrict access, encrypt it when appropriate and set retention and disposal rules. Know where synchronised, exported and backup copies exist. Sending a document to a personal email account or unsanctioned cloud service can bypass every control around the original system.
Back up important data using a design that includes a separate or offline copy. Monitor backup jobs and perform restoration tests. Write down recovery priorities and dependencies. A green “completed” message does not prove that the right data can be restored within the time the organisation needs.
Phishing messages create urgency, imitate trusted people or direct users to unexpected sign-in pages. Verify sensitive requests through a known separate channel. Inspect the actual destination before opening links and report suspicious messages using the approved route. Do not forward a dangerous attachment to colleagues as a warning.
Other warning signs include unexpected multifactor prompts, unknown account changes, disabled security tools, unusual file encryption and unexplained network or billing activity. Disconnecting a device may reduce harm in some incidents, but improvised actions can also destroy evidence or interrupt critical services. Follow the response plan and contact the responsible team quickly.
An incident plan should name reporting channels, decision-makers, technical contacts, communication responsibilities and external obligations. During an event, preserve timestamps and evidence, contain harm, remove the cause, restore from trusted sources and monitor carefully. Record decisions, including uncertainty.
Afterward, identify improvements to technology, process and training. Test the plan with tabletop exercises before a real crisis. A small exercise involving a stolen laptop or compromised email account often reveals missing contact details, unclear authority and untested backups.
Security improves through consistent, verified habits. Begin with assets and risks, use layered controls, make reporting easy and expect systems to fail. The goal is not fear or perfect defence; it is informed preparation that reduces the likelihood and impact of harm.
Keep reading
Educational Resources
The Impact of Digital Twins in Oil & Gas Plant Maintenance is a topic that deserves thorough explora...
Educational Resources
In today’s fast-paced digital landscape, the speed of your WordPress website plays a pivotal role in use...
Educational Resources
Smart homes have transitioned from futuristic concepts to tangible realities that enhance everyday livin...
TAMFIS NIG LTD
Electrical and instrumentation engineering, bid preparation and consulting, IT and software.